Let’s pick up right where Part 1 left off: pfSense Firewall Appliance Unboxing. This isn’t a quick-start guide. It’s my logbook from weeks of fine-tuning pfSense. Weeks, not years, so follow along and let’s learn and improve our pfSense configs together. In this article, I share my pfSense setup: interfaces, firewall rules, pfBlockerNG, Suricata, the… continue reading.
This article is a work in progress and will continue to receive ongoing updates and improvements. It’s essentially a collection of notes being assembled. I hope it’s useful to those interested in getting the most out of pfSense.
pfSense has been pure joy learning and configuring for the for past 2 months. It’s protecting all my Linux stuff, and FreeBSD is a close neighbor to Linux.
I plan on comparing OPNsense next. Stay tuned!
Update: June 13th 2025
Diagnostics > Packet Capture
I kept running into a problem where the NordVPN app on my phone refused to connect whenever I was on VLAN 1, the main Wi-Fi SSID/network. Auto-connect spun forever, and a manual tap on Connect did the same.
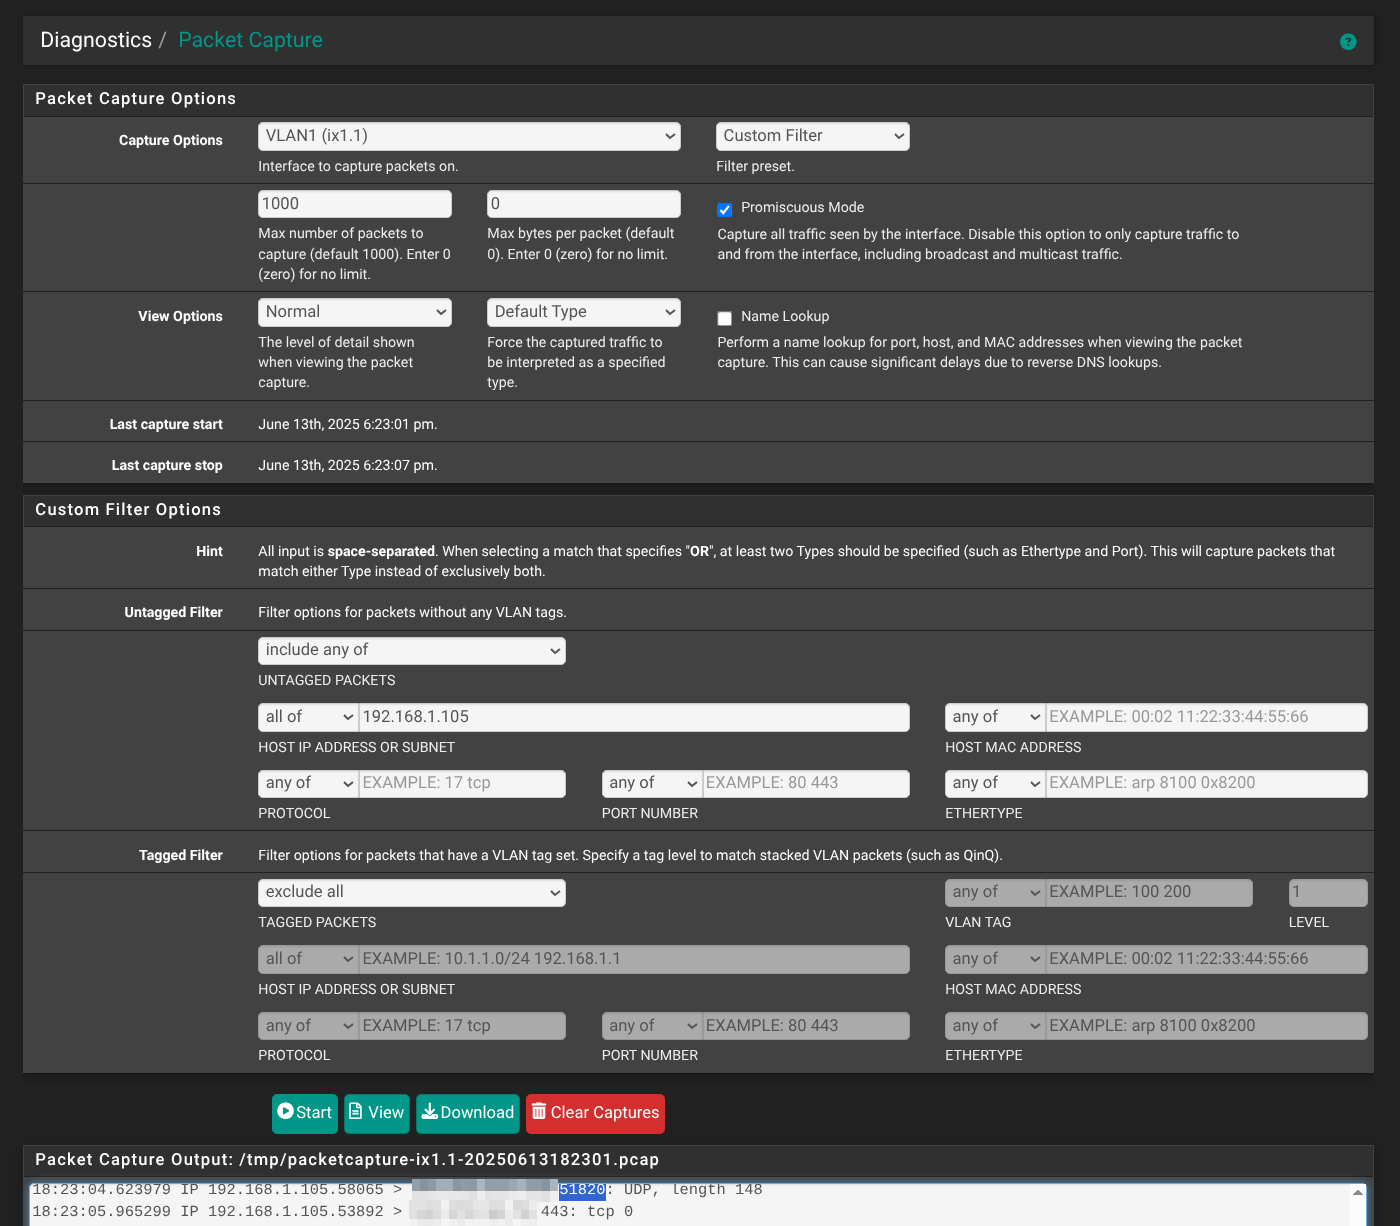
Rather than guess which rule was guilty or missing, I turned to Diagnostics > Packet Capture in pfSense.
1 — Set up a focused capture
Set the following:
- Interface: VLAN 1’s parent (ix1.1 in my case)
- Host IP:
192.168.1.105(my iPhone’s IP address) - Click Start and immediately attempted to connect to NordVPN on my phone.
2 — Stop after 5-10 seconds
That short window is enough to grab the initial handshake. Hit Stop and view or download the capture.
3 — Spot the blocked flow
Opening the file in Wireshark or in this case just scrolling through the plain-text dump showed repeats like:
192.168.1.105 → xx.xx.xx.xx UDP 51820
192.168.1.105 → xxx.xxx.xxx.xxx UDP 51820
UDP 51820 is NordLynx/WireGuard’s default port. Every packet was leaving, none were returning. A clear sign the firewall was dropping them.
4 — Create an allow rule
On VLAN 1 I added one outbound pass rule:

![]()
Action: Pass
Protocol: UDP
Source: VLAN1
Destination port: 51820
The moment the rule went live, NordVPN connected instantly.
Packet Capture is often treated as a heavy-weight troubleshooting tool, but it’s perfect for quick wins like this: isolate one device, capture a short burst, and let the traffic itself tell you which port or host is being blocked.
Update: June 15th 2025
Keeping Suricata lean on a lightly-used secondary WAN
When you bind Suricata to a WAN that only has one or two forwarded ports, loading the full rule corpus is overkill. All unsolicited traffic is already dropped by pfSense’s default WAN policy (and pfBlockerNG also does a sweep at the IP layer), so Suricata’s job is simply to watch the flows you intentionally allow.
That means you enable only the categories that can realistically match those ports, and nothing else.
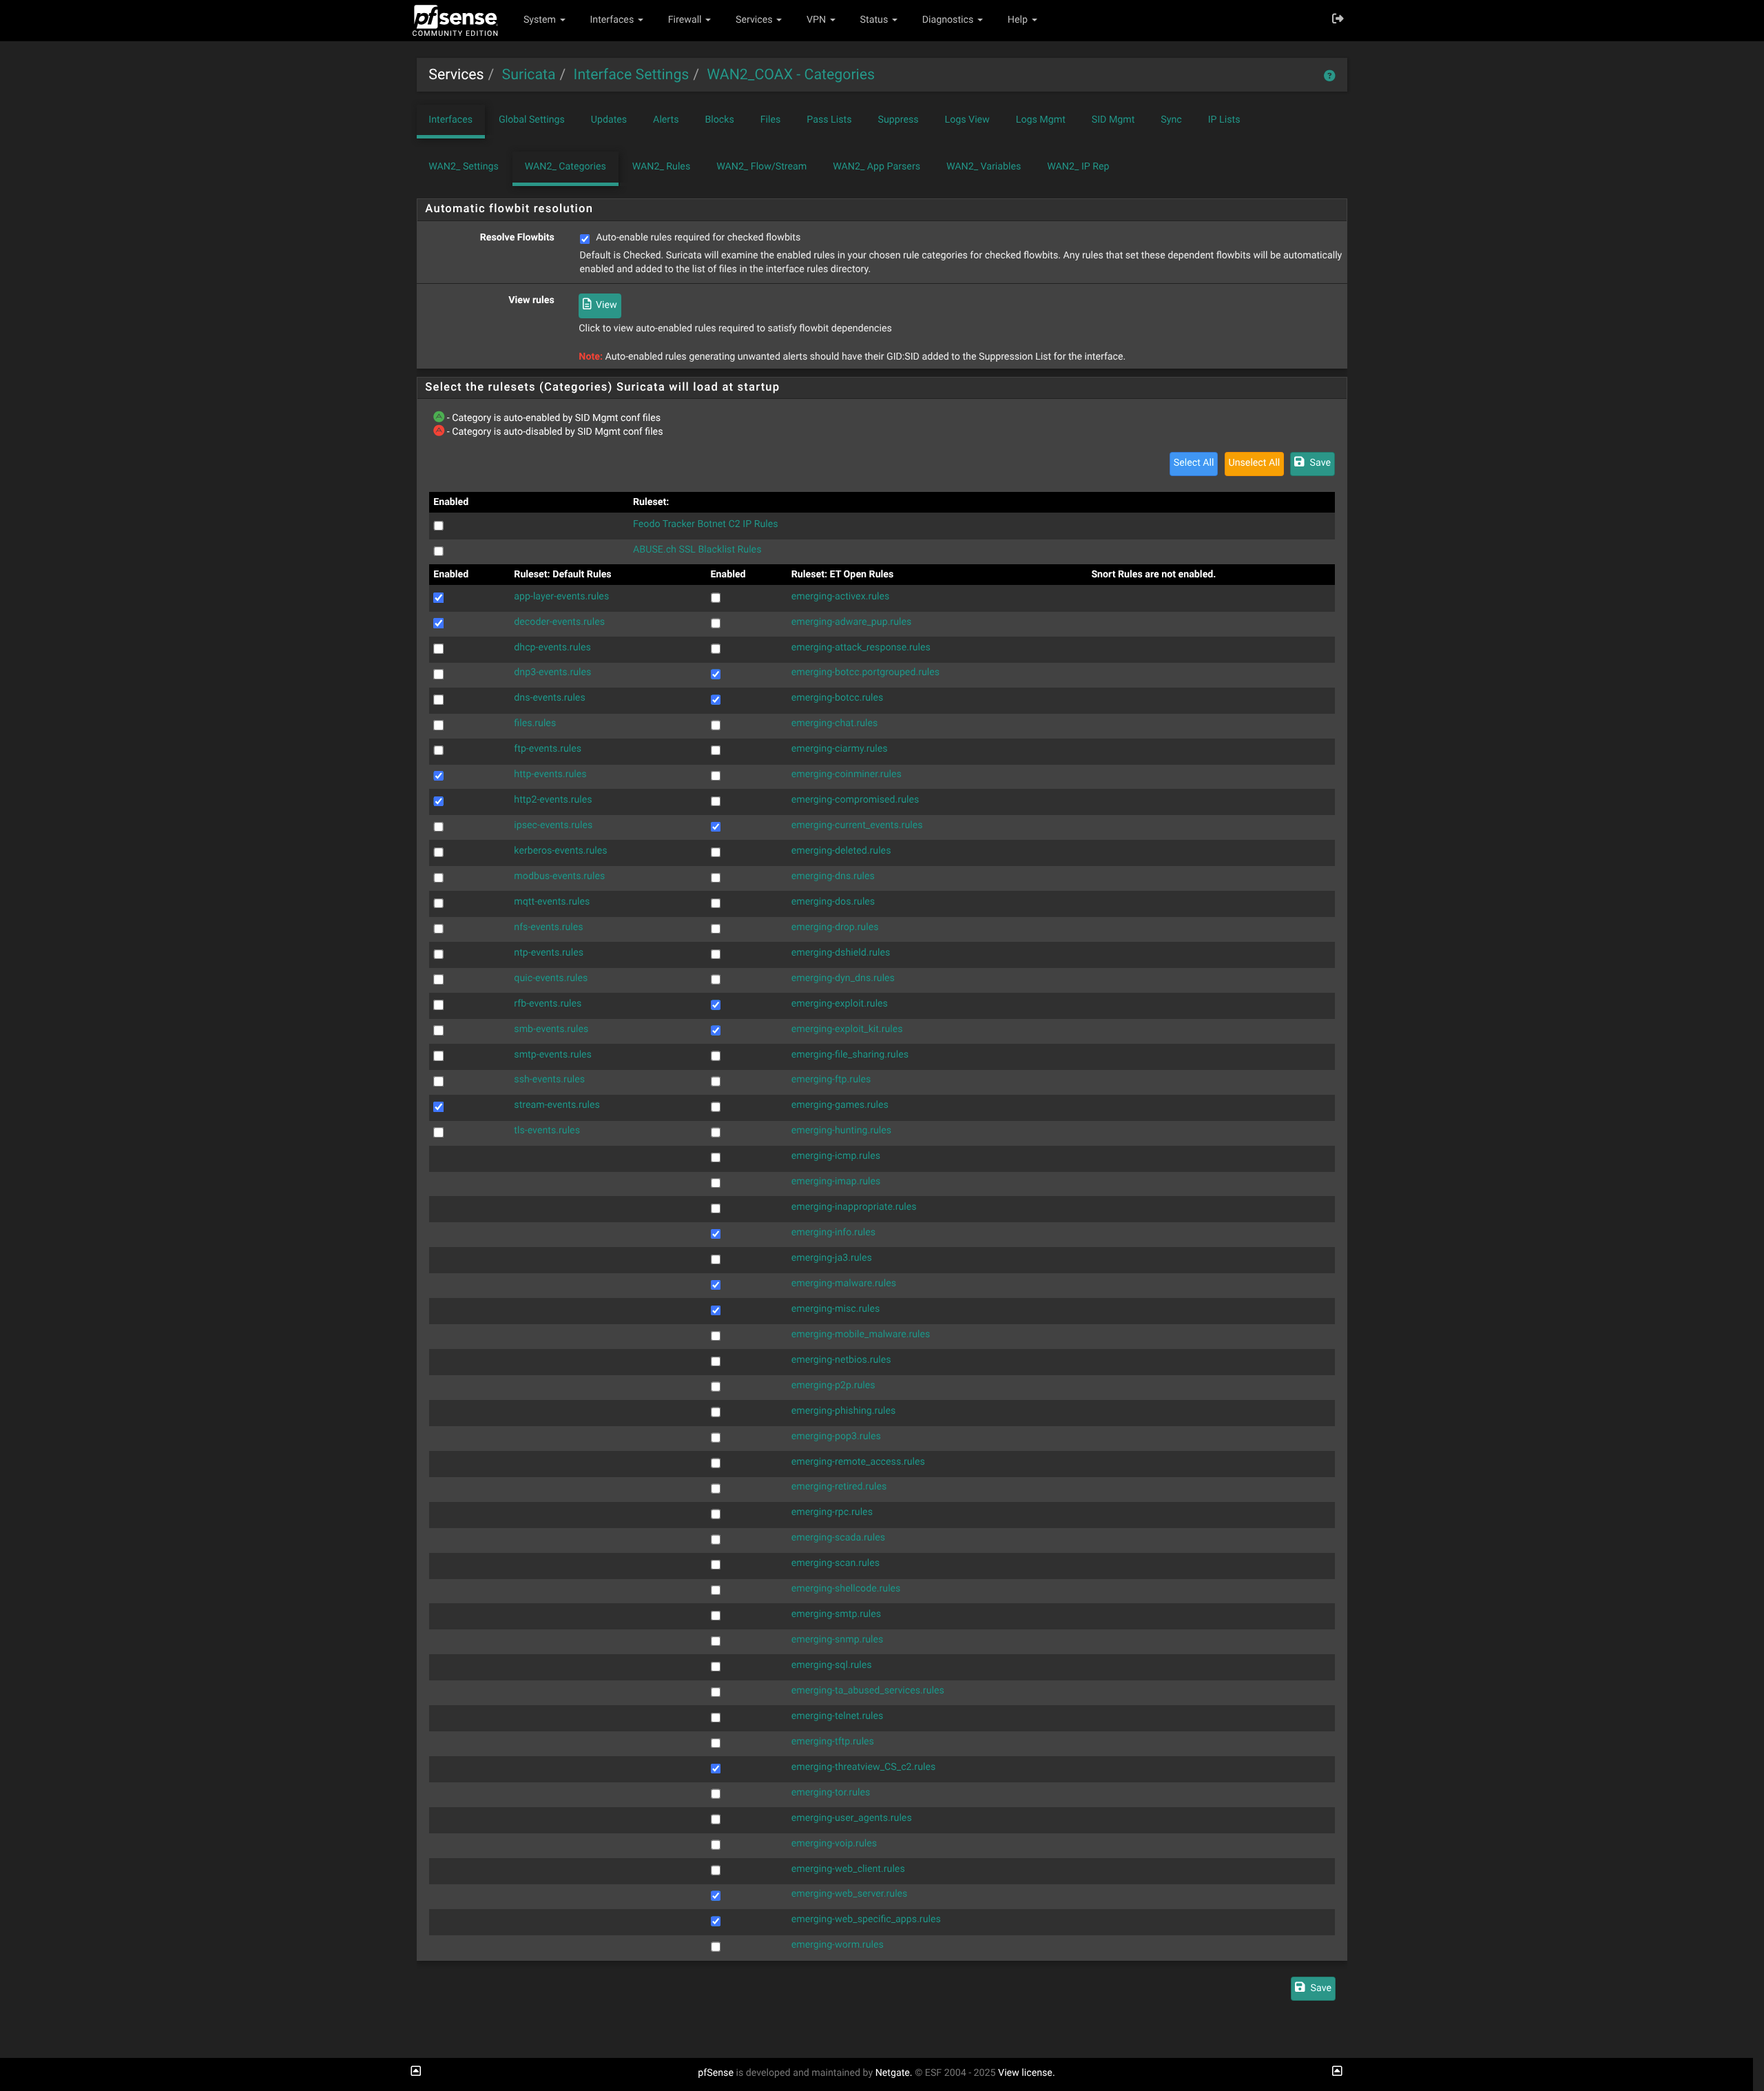
Here’s what that looks like on my backup interface (WAN2):
The ticked boxes in the screenshot boil down to two small groups:
- Core decoder / app-layer helpers –
app-layer-events,decoder-events,http-events,http2-events, andstream-events. These Suricata needs to parse HTTP/S traffic cleanly. - Targeted ET-Open intel –
emerging-botcc.portgrouped,emerging-botcc,emerging-current_events,
emerging-exploit,emerging-exploit_kit,emerging-info,emerging-ja3,
emerging-malware,emerging-misc,emerging-threatview_CS_c2,
emerging-web_server, andemerging-web_specific_apps.
Everything else—mail, VoIP, SCADA, games, shell-code heuristics, and the heavier protocol families, stays unchecked.
The result is a ruleset that compiles in seconds, uses a fraction of the RAM, and only fires when something interesting reaches the ports I’ve purposefully exposed (but restricted by alias list of IPs).
That’s this keeps the fail-over WAN monitoring useful without drowning in alerts or wasting CPU by overlapping with pfSense default blocks.
Update: June 18th 2025
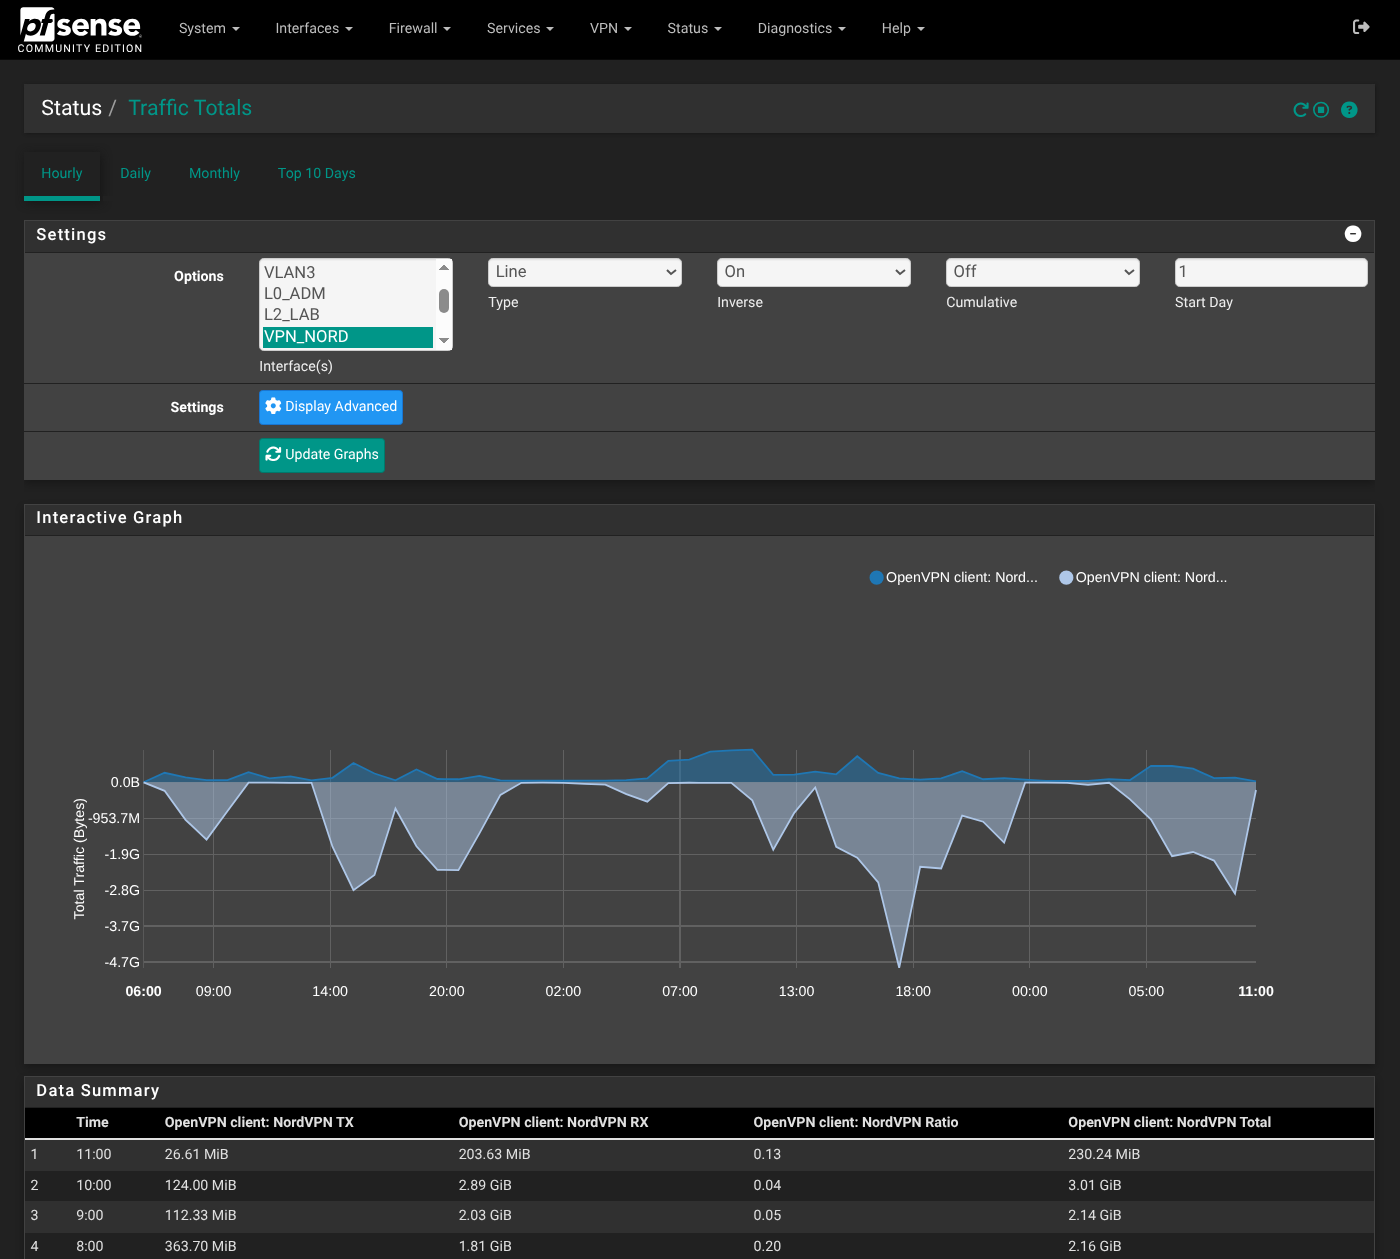
I added a new pfSense package called Status Traffic Totals:
Update: October 7th 2025
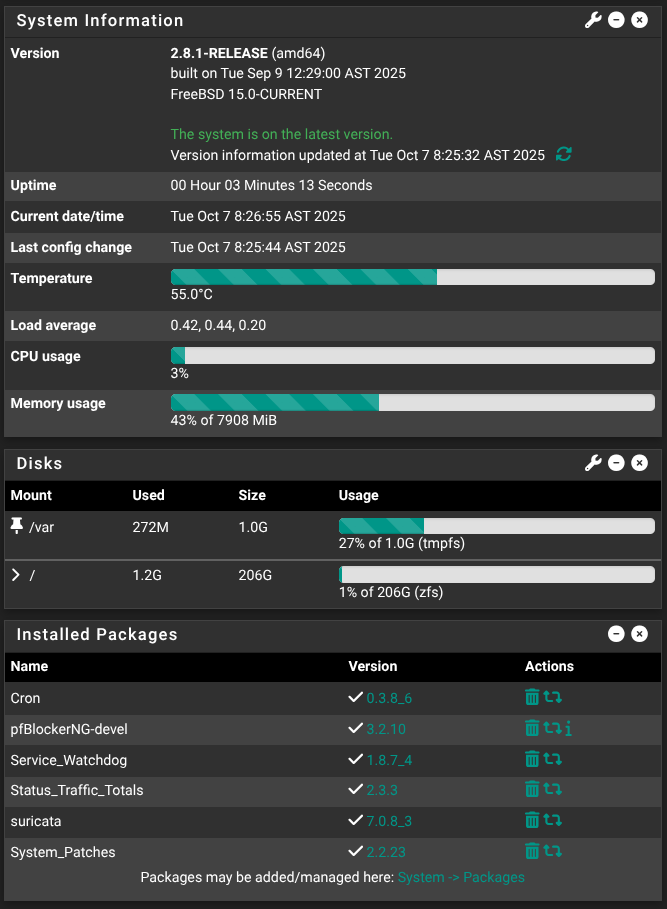
Upgraded to pfSense 2.8.1:
Fantastic article @hydn !
Over the years, the RFC 1918 (private addressing) egress configuration had me confused. I think part of the problem is that my ISP likes to send me a modem one year and a combo modem/router the next year…making this setting interesting.
I see that Netgate has finally published a good explanation and guidance for RFC 1918 egress filtering:
Haha. I know the feeling. Interesting stuff. Would love you hear and see more about your pfSense config/setup sometime.
Did you also already visit the post with my shared config. Any notable similarities or differences?
I have read your pfSense blog, and enjoyed it, but my goals differ.
I use a pair of Netgate 4200 devices, not for high availability, but for hardware isolation.
The first is the edge router/firewall with minimal blocking, but it creates a few DMZ networks:
- work laptop
- OpenWRT and a system I use for monitoring the Internet connection through a cable modem
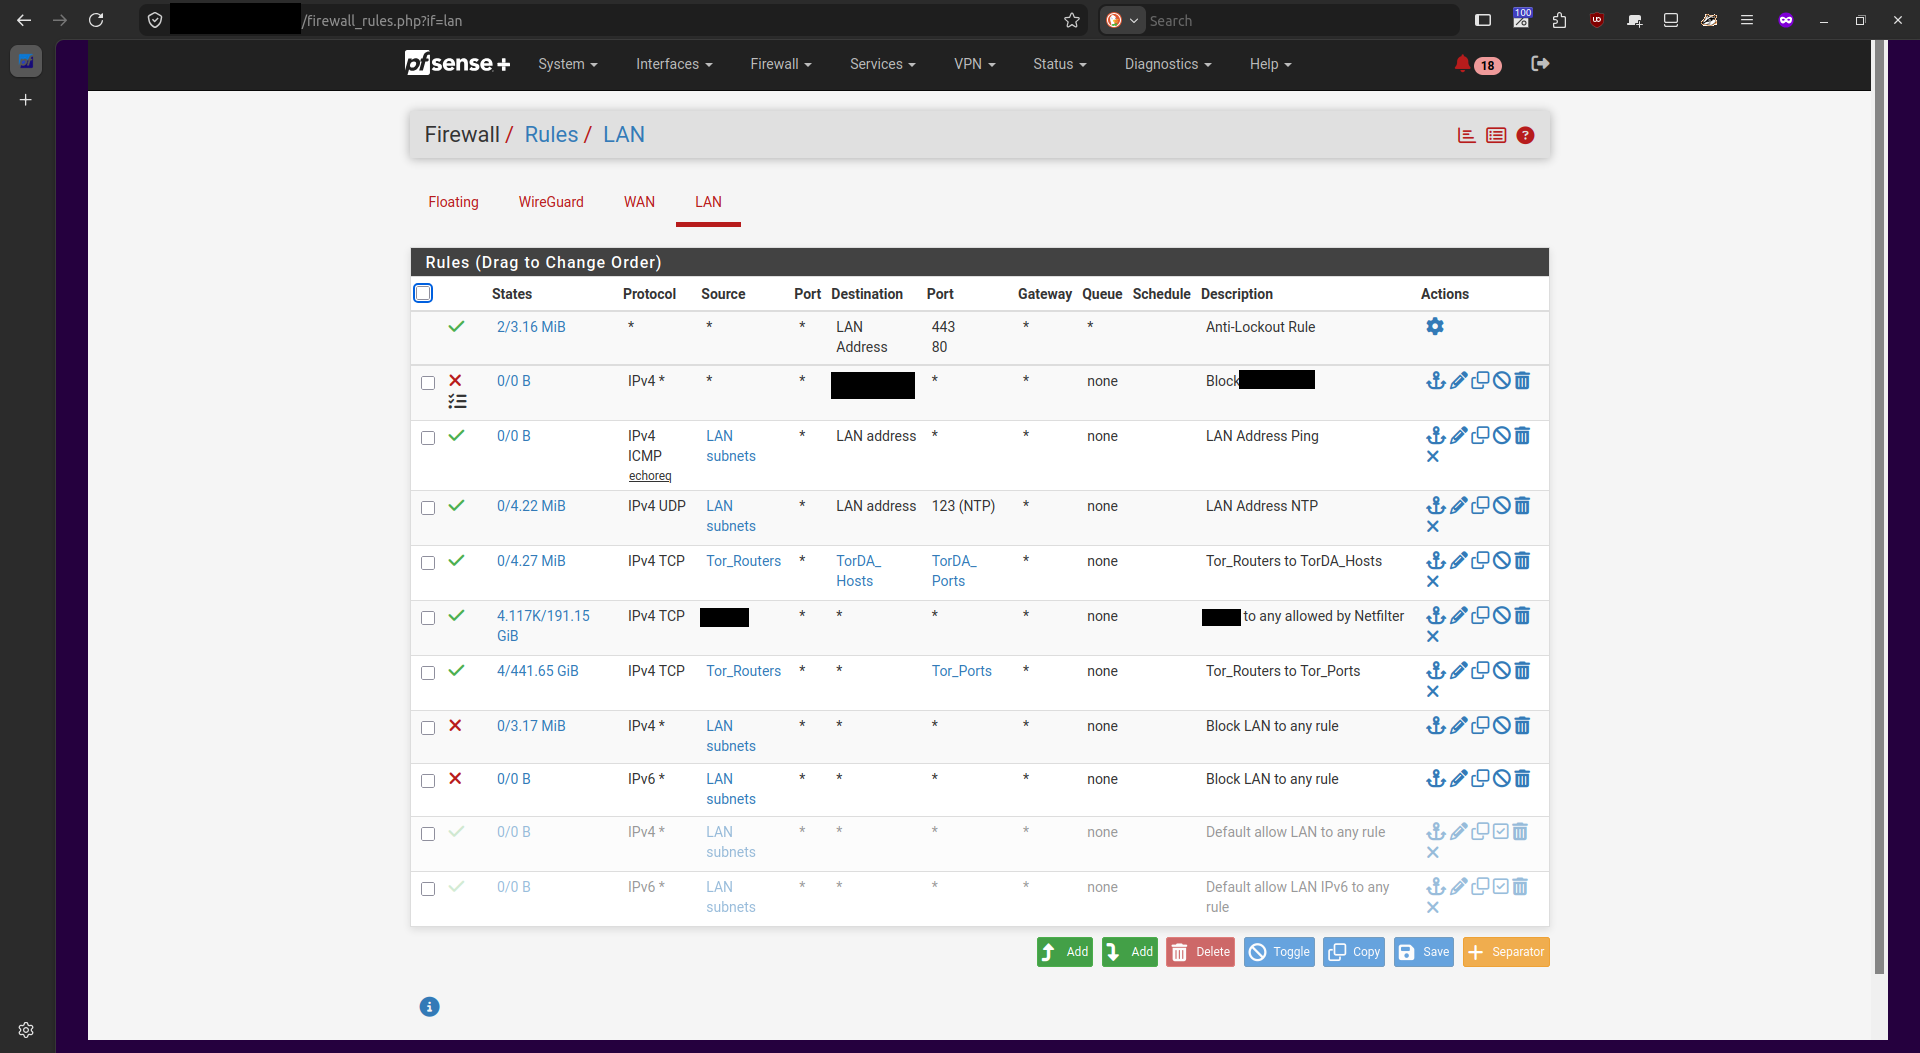
The second is the core router/firewall behind the DMZ network for #2 above. This is the router where basically everything is blocked except traffic that traverses Tor (screenshot).
Alias “Tor_Routers” and alias “Tor_Ports” is for all of the internal Tor clients (some with different configuration for unique goals). Alias “TorDA_Hosts” and alias “TorDA_Ports” are for traffic to the Tor Directory Authorities.
The rule with “Description” of “…to any allowed by Netfilter” works with the Tor relay to allow all internal traffic but only allow traffic to egress to WAN if it uses the service account of the Tor relay’s daemon.
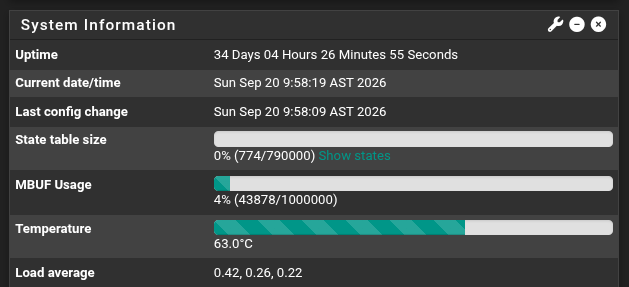
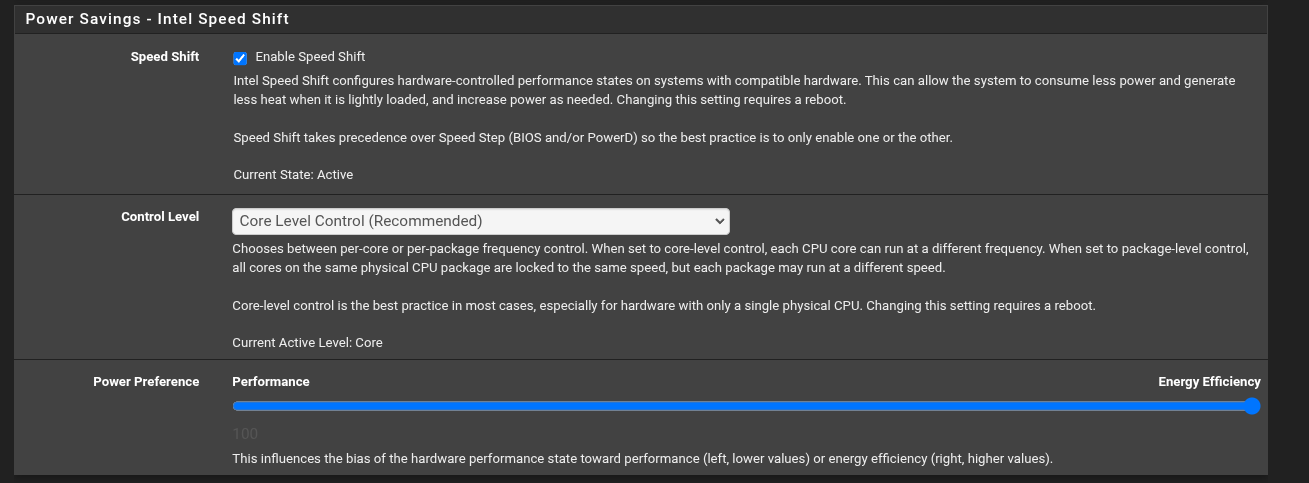
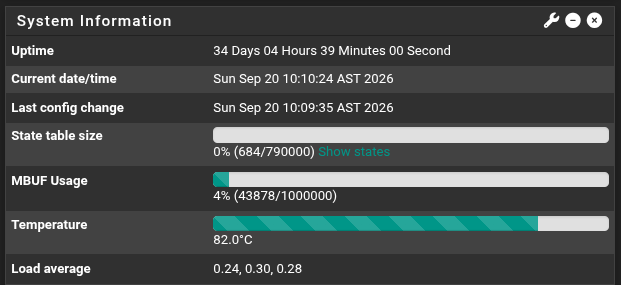
This summer my N100 CPU runs especially hot. I removed the fan that came with it because generally the N100 CPU doesn’t need a fan. Since the load avg is low, before reinstalling the fan, I decided to lower the EPP setting which dropped temps from ~80C to ~60C:
Previously it was set to 50/50 balanced.
I plan to probably lock it in at 80 but am just curious if 100 will have any impact on performance. Mostly in the UI, but no effect on traffic I/O.
Notes:
- The slider is a bias, not a cap. Even at 80 or 100 the CPU will still ramp to FULL speed when traffic needs it. It just doesn’t sit at ~2.9 GHz while idle.
- My firewall runs mostly at < 0.3 load (4 cores), so I won’t notice a throughput difference.
For reference, toggling back to 50/50 looks like this:
I hope this is helpful to anyone else runing pfSense/OPNsense firewall appliance without air conditioning.
I also run pfSense! I’ve been running them on a custom built box for several years now. I am on 2.7.2, which probably explains why I’m not seeing this exact setting (maybe I am looking in the wrong spot).
I tend to not update my firewall often partly because of the large inconvenience of completely taking down my entire network to do so, and partly because I don’t really need any new features (though I’m sure there are security updates I could probably benefit from).
That being said, this feature looks nice, and I’d like to test out how it does on my custom hardware to see if it keeps things even cooler than what they are now. I’m curious to here what impact this has, if any, on your network performance!
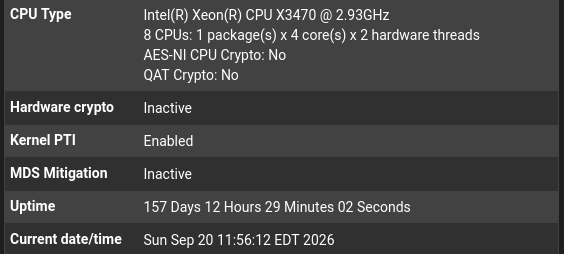
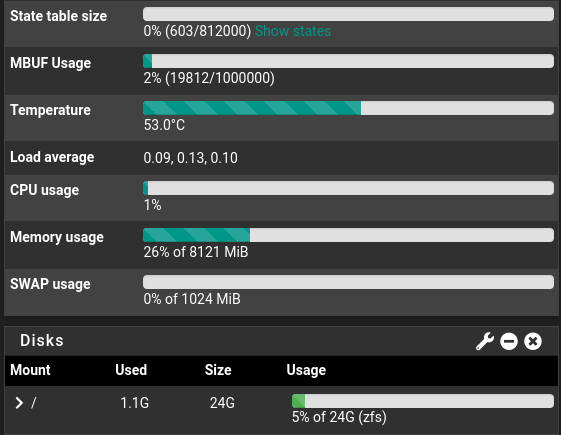
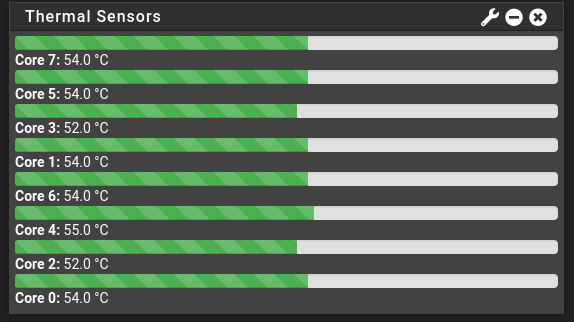
Here’s some screenshots of my pfSense dashboard:
This is where the temps and stats mostly stay. If I’m installing a game from Steam/Epic or downloading a large file, those temps will jump up quite a bit. It’d be cool if those settings prevent that or keep the idles cooler. I’ll plan an upgrade to see what happens.
Pretty cool! I do love pfSense.
The N100 is a 6W CPU, so easier to cool passively. The X3470 is 95W, roughly 16x the heat. So fanless is not realistic. Are those temps without air conditioning in the room?
I specifically choose that CPU because of the challenge of cooling in our region.
Room temp this time of year in the Caribbean was 86 F when I took those screenshots. When I had the fan when I first bought this, I believe it it would sit ~45 C (im sure I may find an old screenshot somewhere), but I don’t remember if I had that slider setting or if it was even set/used. Its been a while.
I have no plans to upgrade to 2.9. I did upgrade to 2.8, but I would have to go back to my previous posts to figure out why upgraded.
I think 4 GB of RAM would have been fine for me also, I overprovisioned on RAM. Just one of the many things I’ve learned about pfSense, and learning.
Yeah, this was the first custom-built box I made. I had a colleague from work help me piece all of the parts together using PCPartPicker to ensure compatibility, then I ordered each of the parts off of eBay individually. Some “new old stock” and some “used”.
I specifically wanted an 8-core CPU and 8GB of RAM because I knew I wanted to run an IDS and other packet-filtering software. I wanted to make sure that all those filters wouldn’t slow down my network tremendously due to CPU/RAM constraints. That being said, I would agree with you. Both the CPU and RAM are over provisioned. I agree with you, I could probably go with a 4-core CPU and 4GB of RAM as well.
I’m over in North Carolina. The average temperature this summer (according to Weather Spark) was 89 degrees Fahrenheit. I keep my A/C on “auto” at 76 degrees Fahrenheit throughout the day. A little warm, but bearable without my electricity bill burning a big hole in my wallet.
So yes, with the house at ~76F, that’s what the average CPU temperature is. It’s still a bit high for my taste. This PC sits in an enclosed old-school rack that I got from a local thrift store (someone mistook it for a wine cooler haha). The circulation in that is not good, and I don’t believe the stock CPU fan is that good either. So I think this was destined to run hotter than it probably should.
I’m planning a new custom built firewall box, so I’m hoping I can get a lower watt CPU with a better CPU cooler to combat those temperatures, but if that setting you pointed out in 2.8 also helps, then I’ll feel much better about where it sits.